button in Safari
Third-Party Software Company Impacted By Online Poker Cyber Attack Issues Statement

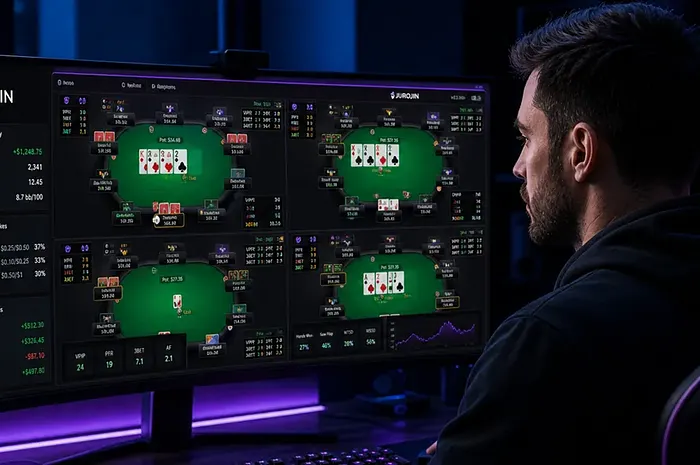
Table Of Contents
New details have emerged in the online poker superuser scandal, as a third-party software company affected has issued a lengthy statement addressing the problem.
Cybersecurity expert @wolfsec0x0, a user on X, exposed a potentially damaging online poker cheating scandal that involved attackers using third-party software to gain access to an online poker player's screen. In doing so, hole cards were exposed to the attacker.
Jurojin Poker, one of two compromised software products, released a lengthy statement explaining the situation, who was impacted, and what the company has done to prevent it from happening again.
What is Jurojin Poker and What Happened?
Only about 30 high-stakes poker players are known to have been targeted. Jurojin has privately contacted all users affected by the attack by email.
Jurojin Poker is an all-in-one productivity tool built for online poker players who want more control over how they play. That means a product that combines table management, hotkey controls, bet sizing tools, and real-time overlays into a single, all-encompassing piece of software that runs alongside your chosen poker client.
At its core, Jurojin helps players act faster, stay more organized at the tables, and generally streamline the process of multitabling, giving them more time and clarity to focus on the decisions that matter. The company's statement read as follows:
This week, our investigation found that between June 2025 and June 2026, an attacker was able to intermittently replace the update package delivered to one specific group of Jurojin users with a tampered version. June 2026 was the last compromised month. Some of those packages included a remote-access tool.
This was a highly targeted operation, not a mass attack. It was carried out by a known cheater aiming at specific opponents, mostly at high stakes, with the goal of viewing their hole cards remotely. Jurojin was one of several applications targeted by the same actor, including IntuitiveTables. The same actor also operated phishing sites impersonating poker rooms and well-known poker tools.
,"
How is Jurojin Responding?
Developers for Jurojin have taken some precautionary measures to ensure a future attack on its software doesn't happen again.
"Our policy of rotating keys frequently, and our other security measures, left the attacker unable to upload anything further. We have logs of every compromised version and the dates it was served, for authorities and security teams," the statement read.
The company also mentioned they had already begun "strengthening security" before learning about the compromised security. Prior to the attack, Jurojin's security team had rotated the encryption keys used between the app and our servers.
"In retrospect, those changes helped mitigate the attacks even though we did not yet know about them," the company admits.
Upon discovering the attack had occurred, Jurojin's security team took additional measures, including restricting access to sensitive configuration, logging every download from the server, and requiring multiple authentication factors in key places where data is edited or deleted on the server.
Jurojin Poker is working with "Wolf," the cybersecurity expert who exposed the online poker attack.
So, how did the attackers successfully target high-stakes online poker players? Here's what Jurojin had to say:
The attacker swapped the update package served to specific users. Some of those packages included a remote-access tool.
We were able to corroborate every historical version of the software that was served, and which of those versions were malicious and which were not. It was always a selective attack on that specific group of players, carried out by hand by the actor, not a mass or automated blast.
We have extensive reports of our findings for authorities and security teams who are interested. Some of them already have those reports.
The Jurojin team closed the statement by apologizing to its users and assuring customers that "security remains a priority."
"For the future, we will be better prepared."